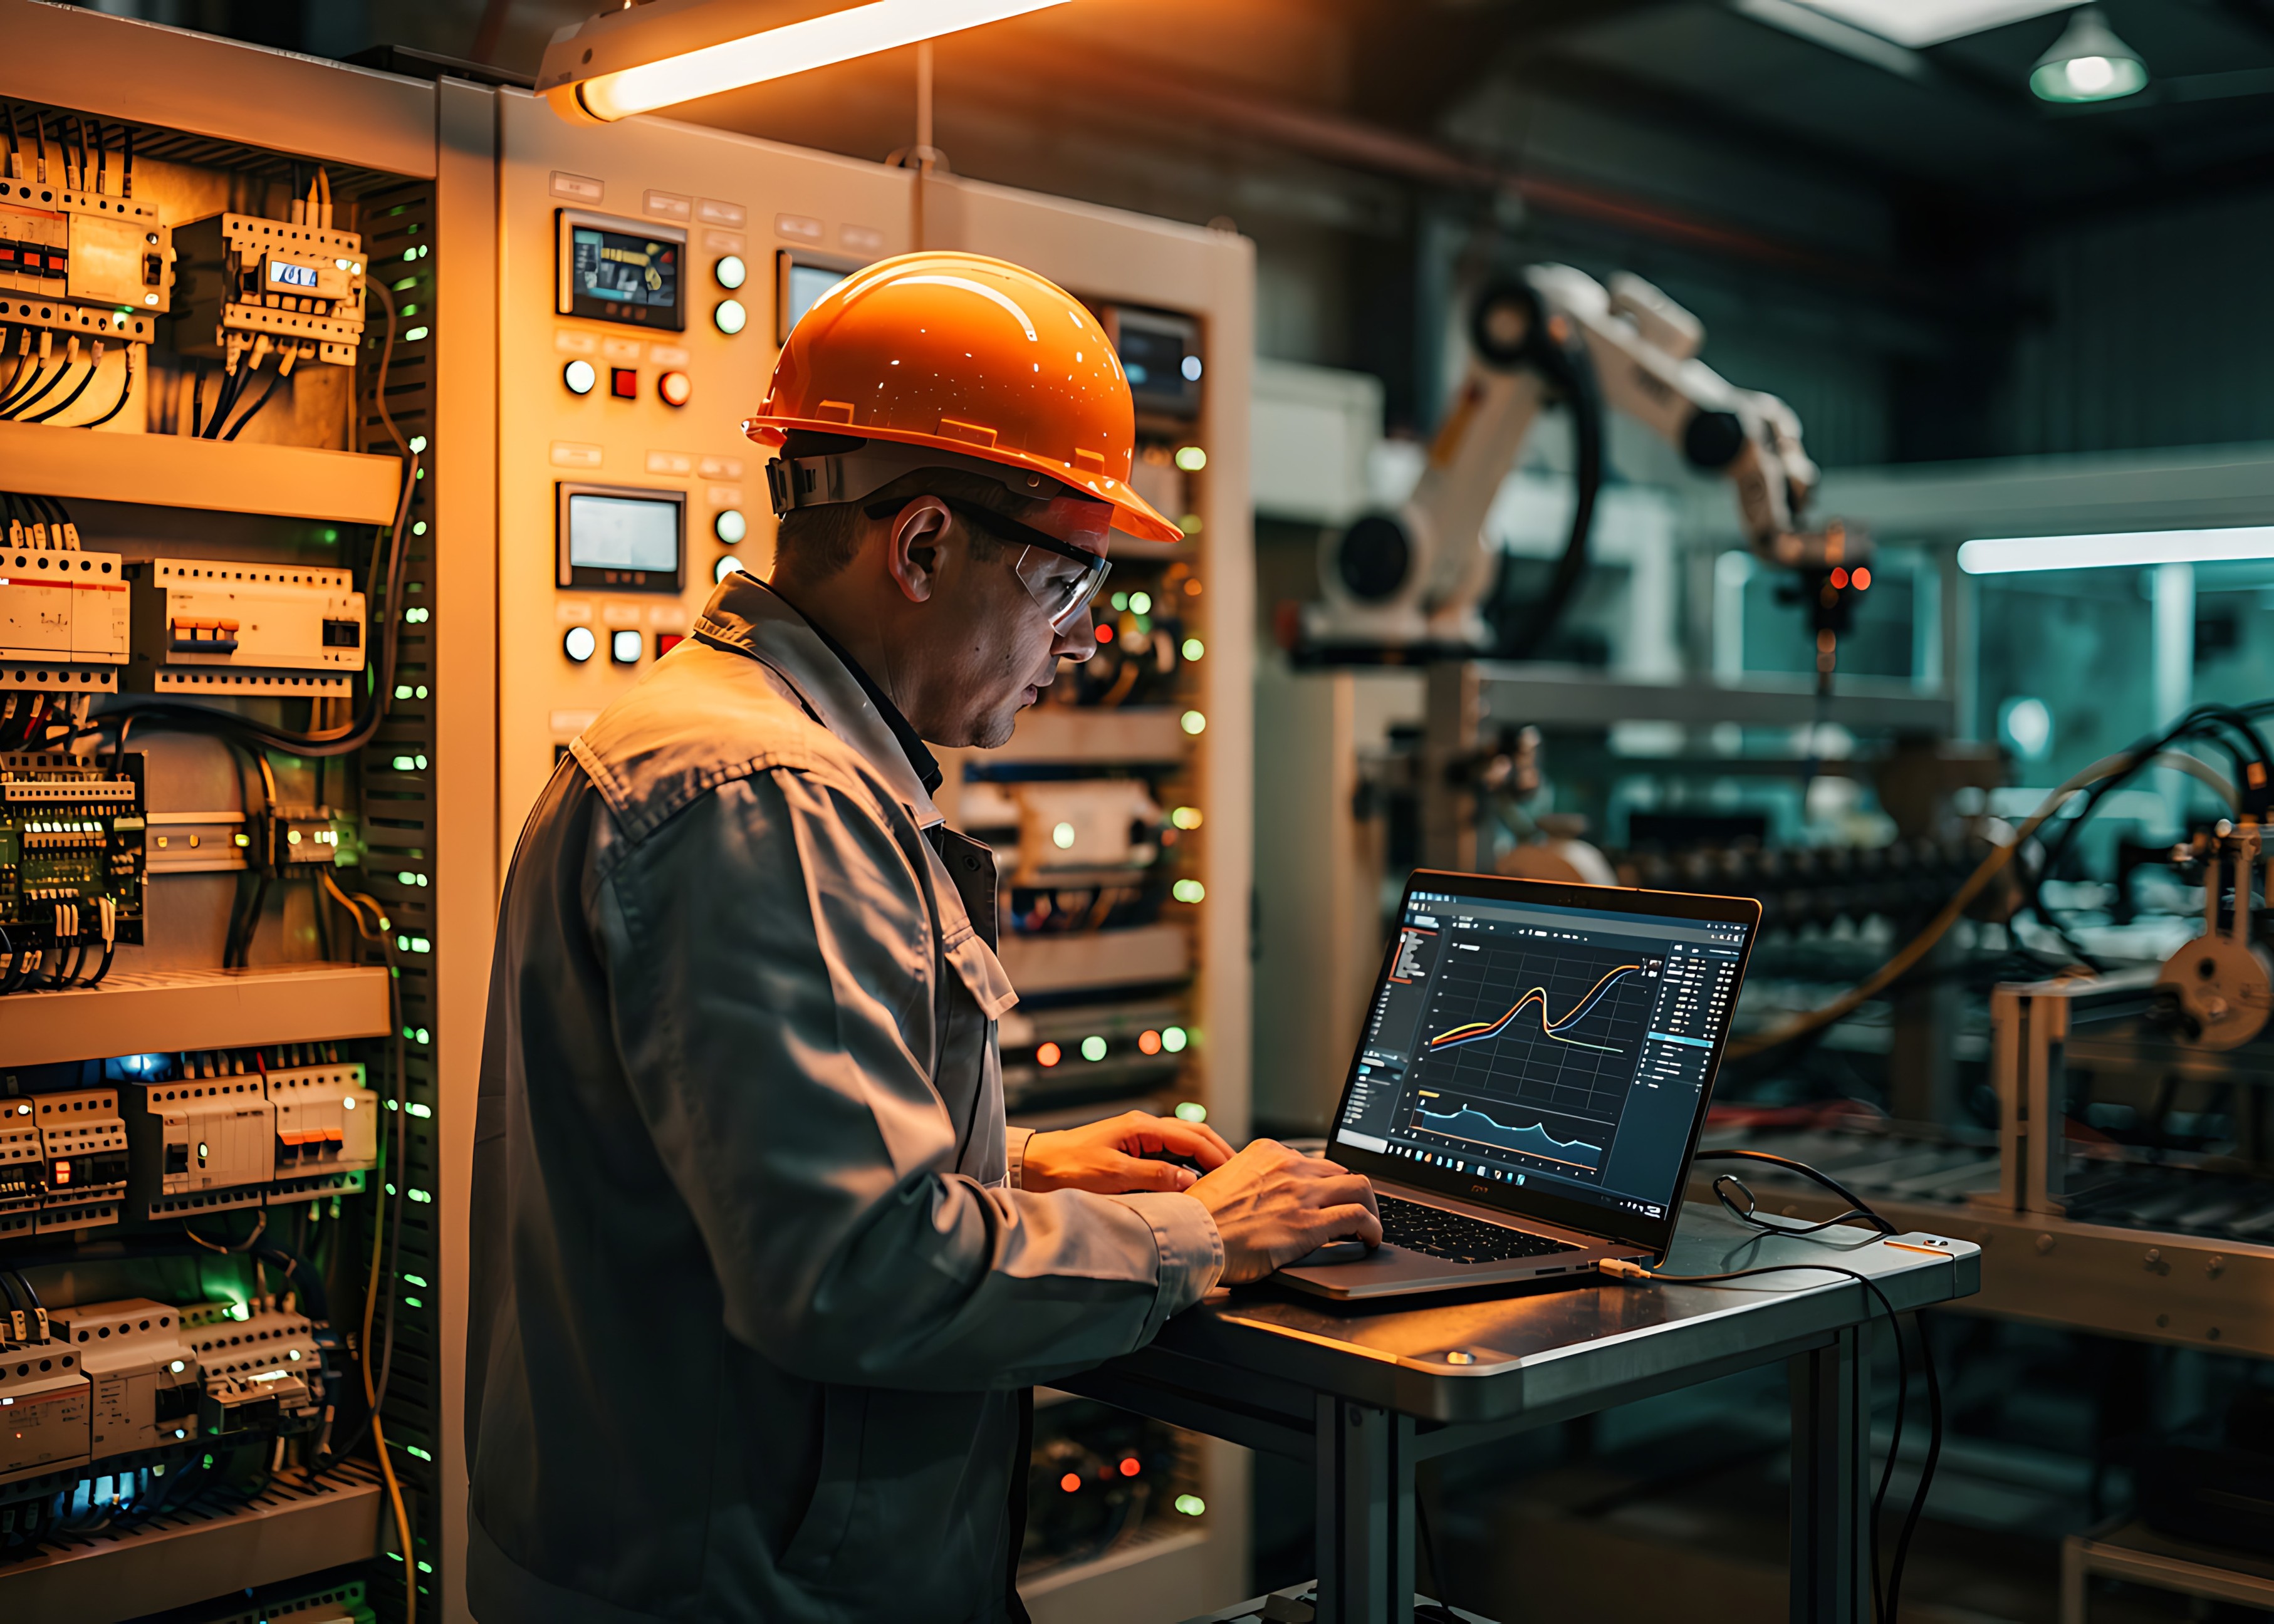
For years, cybersecurity strategies in manufacturing focused primarily on protecting corporate IT systems while keeping production environments largely isolated from external networks. This approach helped limit exposure to cyber threats and allowed OT systems to operate within relatively contained environments. That model is being challenged as manufacturers create more connections between operational technology (OT) and enterprise systems to support business-wide initiatives.
At the same time, the risks are growing: nearly 90% of manufacturers reported production or energy supply impacts from a cyberattack in 2021, and more than one-third of reported attacks affected production operations directly. As a result, cybersecurity is no longer just an IT concern. Attackers are increasingly targeting OT infrastructure, where legacy industrial systems as well as outdated communication protocols and data architectures can create attractive entry points into critical operations.
As manufacturers accelerate digital transformation initiatives and invest in AI, analytics, automation, and connected operations, OT environments are becoming more interconnected than ever before. More assets are online, more applications require access to operational data, and more information is moving between the plant floor and enterprise systems. While this connectivity creates new opportunities, it also expands the attack surface and exposes long-standing vulnerabilities that many organizations have yet to address.
Shift from IT-centric threats to OT-focused attacks
Manufacturing organizations have become increasingly attractive targets for cybercriminals. Cyberattacks and ransomware incidents have increased significantly across industries, while known attacks on OT and industrial control system networks continue to impact physical sites. These attacks are no longer limited to stealing information or disrupting office productivity. In OT environments, cybersecurity incidents can interrupt production, impact product quality, disrupt supply chains, and create safety concerns for workers and facilities.
What makes OT particularly vulnerable is its reliance on infrastructure that was never designed for today's connected environments. Many manufacturing facilities continue to operate legacy equipment and communication technologies that prioritize reliability and uptime over security. As organizations connect these systems to enterprise applications, cloud platforms, and AI initiatives, vulnerabilities that once existed only within isolated networks become potential pathways for external threats.
Legacy protocols create modern risks
One of the most common challenges facing industrial organizations is the continued use of legacy communication protocols. Many were designed decades ago for isolated systems and trusted environments. They were not built to support modern cybersecurity requirements, nor were they designed to securely exchange information across increasingly connected IT and OT ecosystems. The challenge is compounded by the diversity of industrial environments. Facilities often contain a mix of legacy and modern assets, each communicating through different protocols and interfaces. As organizations attempt to bring data together for monitoring, performance management, analytics, or AI applications, they frequently rely on custom integrations and direct connections between devices and applications. These point-to-point architectures can create a complex web of dependencies that becomes increasingly difficult to secure, maintain, and scale.
In these environments, every custom integration introduces another potential attack surface. Disparate protocols, inconsistent data models, and fragmented communication paths can make it difficult to apply consistent security policies, standardize access controls, and monitor data flows across the enterprise. As connectivity grows, so does the complexity of managing risk.
Increased integration is expanding the attack surface
The increase in connected devices and applications is accelerating this challenge. Manufacturers are connecting more machines, sensors, PLCs, and other operational assets to support business initiatives that depend on industrial data. At the same time, OT data is being consumed by a growing number of systems, including manufacturing execution systems, enterprise applications, cloud platforms, analytics environments, and emerging AI solutions. Without a standardized approach to connectivity, organizations often respond by creating additional one-off integrations. New devices require connections into multiple applications, while new applications require direct access to multiple data sources. The result is an architecture that becomes increasingly difficult to govern, monitor, and secure.
The consequences extend beyond cybersecurity. Fragmented connectivity can slow access to operational data, strain infrastructure through excessive polling, weaken governance efforts, and limit the ability to establish consistent context across systems. These challenges ultimately affect an organization's ability to scale digital initiatives effectively.
Regulatory pressure is raising the stakes
As threats evolve, regulators are responding. One of the most significant developments is the European Union's Network and Information Systems Directive 2 (NIS2), which expands cybersecurity expectations for organizations operating within critical industries and essential services. The directive places greater emphasis on security requirements, incident reporting, supply chain security, and organizational accountability. Importantly, the implications extend beyond technical teams. NIS2 increases organizational accountability by requiring management bodies to approve cybersecurity risk-management measures and oversee their implementation. It also introduces stronger incident-reporting obligations and significant financial penalties for noncompliance, while giving authorities broader supervisory and enforcement powers. As a result, OT cybersecurity is increasingly becoming a boardroom concern rather than solely an operational or technical issue.
Whether organizations operate in water and wastewater, food and beverage, pharmaceuticals, transportation, energy, or manufacturing sectors, cybersecurity resilience is now closely tied to operational continuity, regulatory compliance, and business risk management.
Building a secure ot data foundation
Addressing OT cybersecurity challenges requires more than deploying additional security tools. Organizations must evaluate the underlying architectures that govern how operational data moves throughout the enterprise.
Several foundational practices can support stronger OT security, such as maintaining accurate inventories of OT assets, conducting risk assessments, implementing strict access controls, maintaining system integrity, and developing incident response capabilities. However, modernizing and securing the architecture itself is the key to lasting, enterprise-wide impact.
A key component of modernization is introducing a standardized connectivity layer between industrial assets and consuming applications. Rather than creating direct device-to-application integrations, organizations can establish a consistent framework for connecting, normalizing, securing, and managing OT data. This approach reduces dependence on fragmented point-to-point architectures while improving visibility and control.
Standardized connectivity also supports the adoption of more secure communication methods, simplifies policy enforcement, and enables more consistent governance across facilities. Combined with network segmentation and access management practices, it can help limit lateral movement, reduce exposure to protocol-level vulnerabilities, and improve the overall resilience of OT environments.
Security and AI share the same foundation
The continued growth of industrial AI introduces another important dimension to the OT cybersecurity conversation. AI, analytics, and automation initiatives all depend on reliable access to operational data. Yet the same fragmented architectures that create cybersecurity risks can also limit the effectiveness of these technologies. Data that is inconsistent, difficult to access, lacking context, or spread across numerous point-to-point integrations presents challenges for both security teams and AI initiatives. Conversely, standardized data movement, consistent architectures, and governed access help organizations establish a foundation that supports both cyber resilience and digital transformation goals.
In this sense, OT cybersecurity and AI readiness are increasingly interconnected objectives. Secure, scalable data architectures help organizations reduce risk while ensuring operational data can be used effectively across business systems, analytics platforms, and future AI applications.
The future of OT security starts with the data foundation
The assumption that cybersecurity begins and ends with IT no longer reflects today's industrial reality. As manufacturers connect more devices, increase data sharing, and expand digital initiatives, attackers are finding new opportunities within OT environments. Legacy systems, outdated protocols, and fragmented connectivity architectures are becoming high-value targets because they often represent the weakest link in otherwise modern operations. Addressing these risks requires cybersecurity to become a shared responsibility across IT and OT. IT teams bring established security practices and enterprise-wide oversight, while OT teams bring essential knowledge of industrial assets, processes, and operational requirements. By working together, they can apply cybersecurity best practices in ways that strengthen protection without compromising the reliability and continuity of critical operations.
Organizations that proactively modernize connectivity, standardize data movement, and strengthen the security of OT architectures will be better positioned to reduce risk, meet evolving regulatory requirements, and support future digital transformation initiatives. In an era where cybersecurity, operational resilience, and AI readiness are increasingly intertwined, building a secure OT data foundation has become a strategic imperative rather than a purely technical exercise.