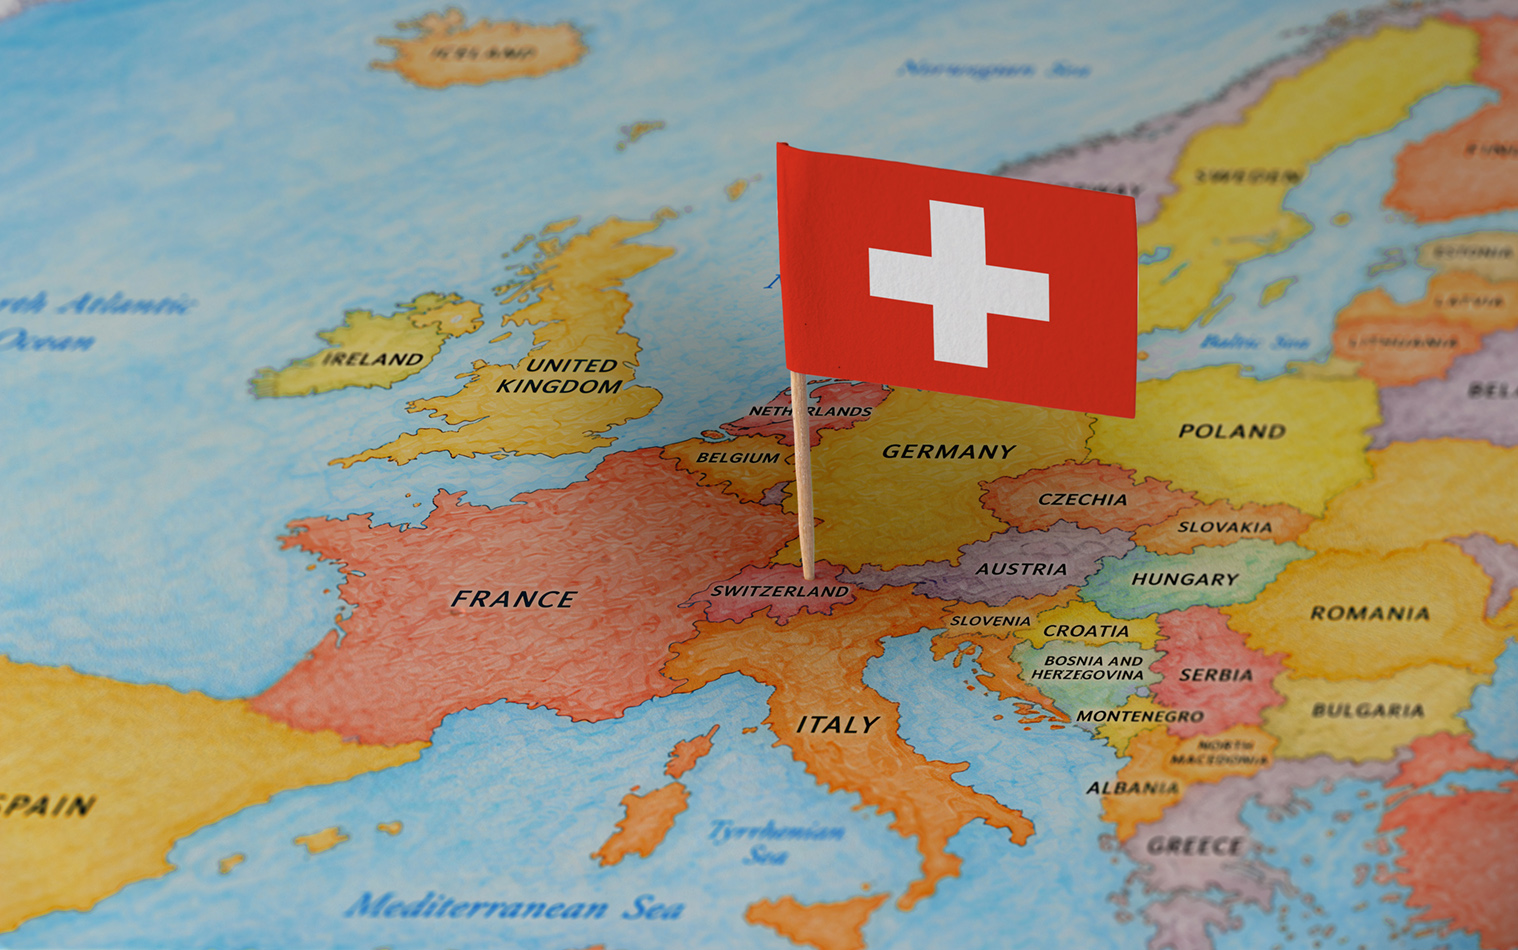
Switzerland has an interesting relationship with European regulation. Geographically, we are in the middle of Europe and economically deeply integrated into European supply chains. Politically and legally, however, Switzerland is not an EU member and follows its own regulatory path.
The EU Cyber Resilience Act (CRA) is a good example of why this distinction can be less clear in practice than it appears on a map. From a Swiss industrial and automation perspective, I see five questions worth asking.
1. Does the CRA matter if Switzerland is not in the EU?
Initially, it depends on where you sell your products. A Swiss manufacturer serving only the Swiss market is in a different position than one exporting to the EU. As soon as a product is placed on the EU market, the CRA comes into play.
The CRA covers a broad range of products with digital elements, including programmable logic controllers (PLCs), gateways and human-machine interfaces (HMIs). For export-oriented Swiss manufacturers, the practical question is therefore not simply “Does the CRA apply in Switzerland?” but “What would it mean if we could no longer sell our products into the EU?” Considering that approximately half of Swiss exports go to the EU, this is relevant to many manufacturers.
Most CRA requirements become applicable in December 2027, while reporting obligations for actively exploited vulnerabilities and severe security incidents have applied since 11 September 2026. Even for Swiss-only suppliers, the CRA may increasingly define what customers consider an adequately secure product.
2. Who will pay for the additional cybersecurity?
Secure development, testing, vulnerability monitoring, incident handling, security updates and long-term support all cost money. Some of that will inevitably be reflected in product prices.
A manufacturer could theoretically maintain a cheaper Swiss product and a CRA-compliant EU version. In practice, maintaining separate software, documentation, vulnerability handling and lifecycle processes creates costs of its own.
For manufacturers with significant European business, one secure development process and essentially the same product on both sides of the border will often make more sense. The CRA may therefore influence products and prices in Switzerland without being subject to Swiss law.
3. Will Swiss customers deliberately buy the cheaper alternative?
Industrial equipment often remains in operation for 20 years or more. By then, the original engineering workstations, software and even some suppliers may no longer be around.
This makes the CRA’s support-period requirement particularly relevant. The support period should reflect the expected product lifetime and is generally at least five years. For industrial products expected to operate much longer, five years alone may clearly not be enough.
Swiss operators can address this directly in tenders: require the supplier to declare the expected product lifetime and cybersecurity support period, explain how vulnerabilities will be handled and define how security updates will be provided.
If a product already reflects CRA requirements because it is also sold in the EU, there is little reason not to make those expectations explicit in a Swiss tender as well.
4. Will Switzerland eventually introduce its own CRA?
The process has already started.
In August 2025, the Swiss Federal Council instructed the Federal Office for Cybersecurity, together with Ofcom and SECO, to prepare legislation on the cyber resilience of products with digital elements. A consultation draft is expected by autumn 2026.
The planned legislation is intended to introduce cybersecurity requirements for digital products, establish market surveillance and provide a basis for prohibiting the import and sale of insecure products. The Federal Council has also explicitly stated that the international context, including the EU CRA, should be taken into account while avoiding unnecessary burdens and conflicting requirements for internationally active Swiss companies.
The Swiss approach does not have to be identical to the CRA, but some degree of alignment appears both likely and practical.
5. Where does ISA/IEC 62443 fit into all of this?
Fortunately, industrial automation does not have to start from zero. The ISA/IEC 62443 series has addressed secure development, threat modeling, security verification, vulnerability management, patch management and defense in depth for many years.
However, ISA/IEC 62443 compliance does not automatically mean CRA compliance. The CRA is legislation. ISA/IEC 62443 is an international standards framework. They overlap considerably, but their scope and conformity mechanisms are not identical.
Manufacturers already working according to ISA/IEC 62443 therefore have a strong foundation. The ongoing revisions of harmonized European Norms (hEN) IEC 62443-4-1 and 62443-4-2 will also be important in keeping the series relevant as regulatory expectations evolve.
The objective should not be to turn ISA/IEC 62443 into a copy of the CRA. As an international standard, it must remain applicable across jurisdictions.
Conclusion
The CRA may be an EU regulation, but its impact will not stop at the EU border. For Swiss manufacturers exporting to Europe, cybersecurity is becoming part of market access, just as safety, quality and product conformity have been for decades.
For Swiss end users, the practical questions are equally important: What cybersecurity level are we buying? How long will it be supported? And who will still be responsible for vulnerabilities when the equipment is 10, 15 or 20 years old?
Switzerland is developing its own regulatory response to product cybersecurity. For industrial automation, ISA/IEC 62443 continues to provide an established international framework for cybersecurity practice.
For Switzerland, the question is therefore not whether the CRA will have an impact, but how we choose to respond to it. After all, cyber attackers care about national borders about as much as they care about organizational boundaries within a company.