


©2026 Automation.com, a subsidiary of the International Society of Automation.
-
 ISA provides technical resources and standards to help industrial automation professionals advance their careers and the field. We enable automation professionals worldwide to solve problems and enhance their skills by bringing people together to create new technologies and share best practices with future automation professionals.
-
ISA Resources
-
Upcoming Events
-
Industry Insights
-
Consortia
-
Articles and News
255 Results Found
-
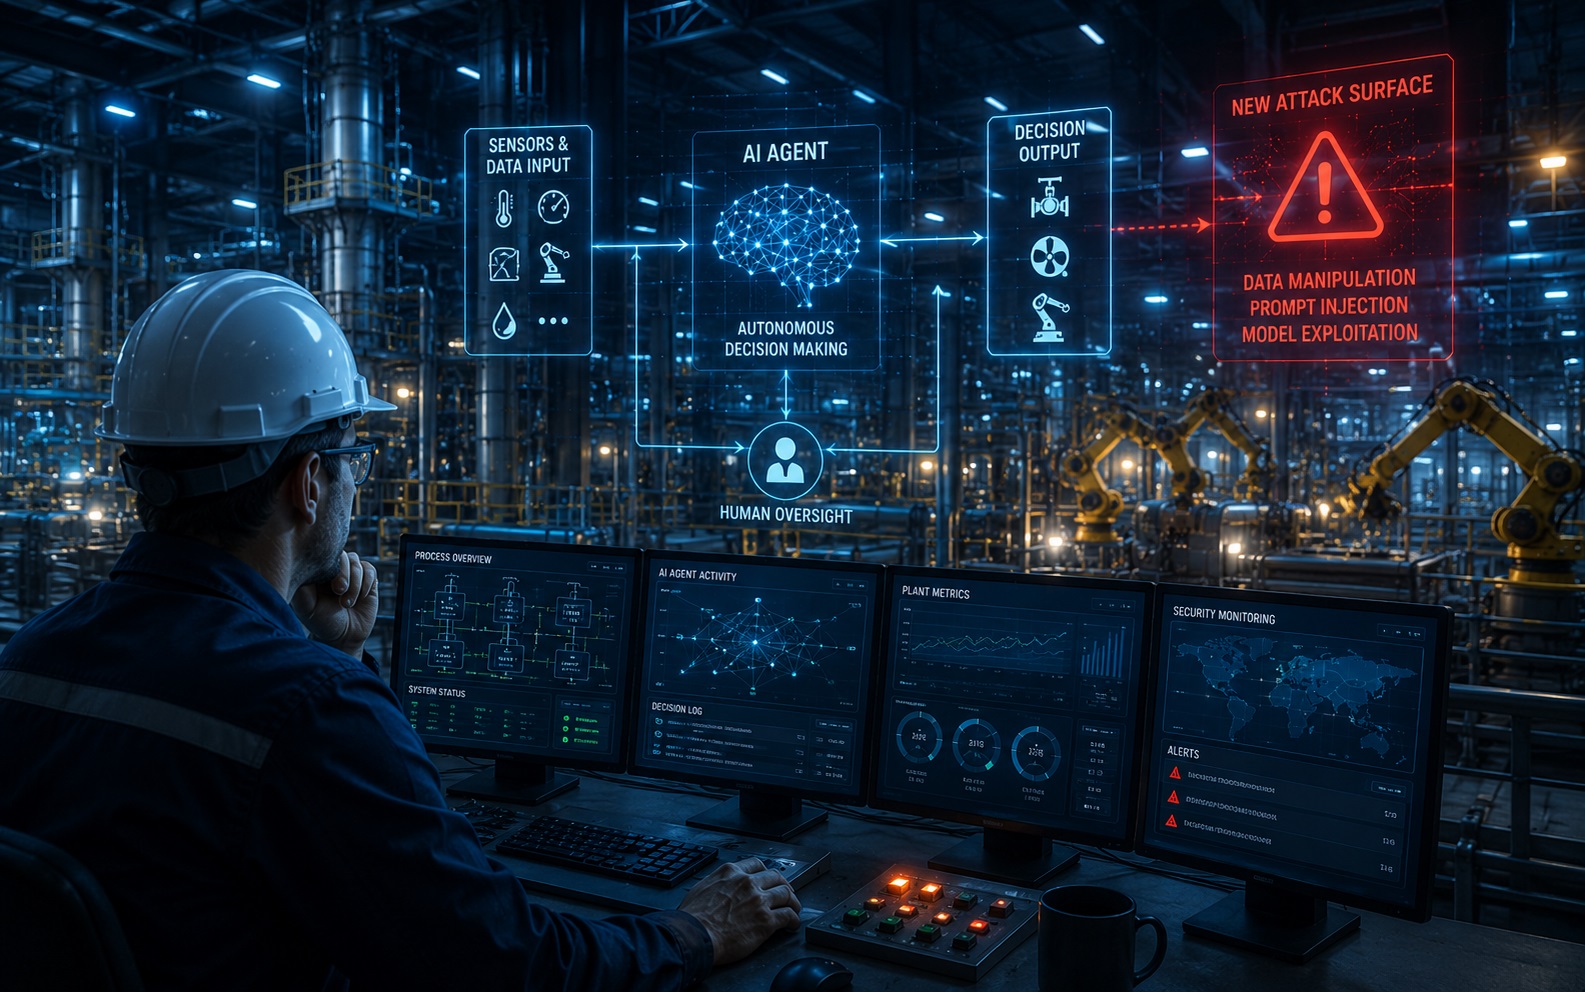
Securing New Threats: Industrial AI-Powered Applications and Autonomous Agents
Treat AI engines as high-risk zones, adapt frameworks such as ISA/IEC 62443, and keep humans actively in the loop. -
The EU Cyber Resilience Act: What Does It Mean for UK Suppliers?
The CRA may influence suppliers, asset owners and customers to expect cybersecurity to become a product characteristic throughout its lifecycle. -
From the Editor: Keeping Up with OT Cybersecurity Trends
Welcome to the October 2026 issue of the International Society of Automation’s online magazine, Automation.com Monthly, the annual roundup of OT Cybersecurity Trends. Learn how to secure connected legacy systems, prepare to resist quantum-computer-enabled decryption, manage end-of-life IoT devices, and more. Discover what the EU Cyber Resilience Act means for asset owners and automation suppliers. Access global research on industrial cybersecurity vulnerabilities, mitigations, and protection strategies. Discover resources for staying up to date on OT cybersecurity strategies at every level. -
A Practical Path to Post-Quantum Readiness in Operational Technology
How to develop an OT cybersecurity roadmap to transition to PQC algorithms designed to resist quantum-computer-enabled decryption. -
Rockwell Automation Research Reveals More Than One-Third of Industrial Organizations See Cybersecurity Risk as a Top Obstacle to Growth
Industrial companies are increasing cybersecurity investment as connected operations, AI adoption and IT/OT convergence expand operational risk. -
DeNexus Joins ISA Global Cybersecurity Alliance to Facilitate Broad Adoption of OT Cybersecurity Standards
The ISA/IEC 62443 framework, along with DeNexus’ expertise, will enable industries to assess, quantify and assign a cost to risk. -
The Cyber Resilience Act: Compliance Starts with Product Security, Not Documentation
Implementing the CRA is an opportunity to achieve higher levels of product security maturity by actively anticipating and preparing to address security issues that may arise throughout a product’s lifecycle. -
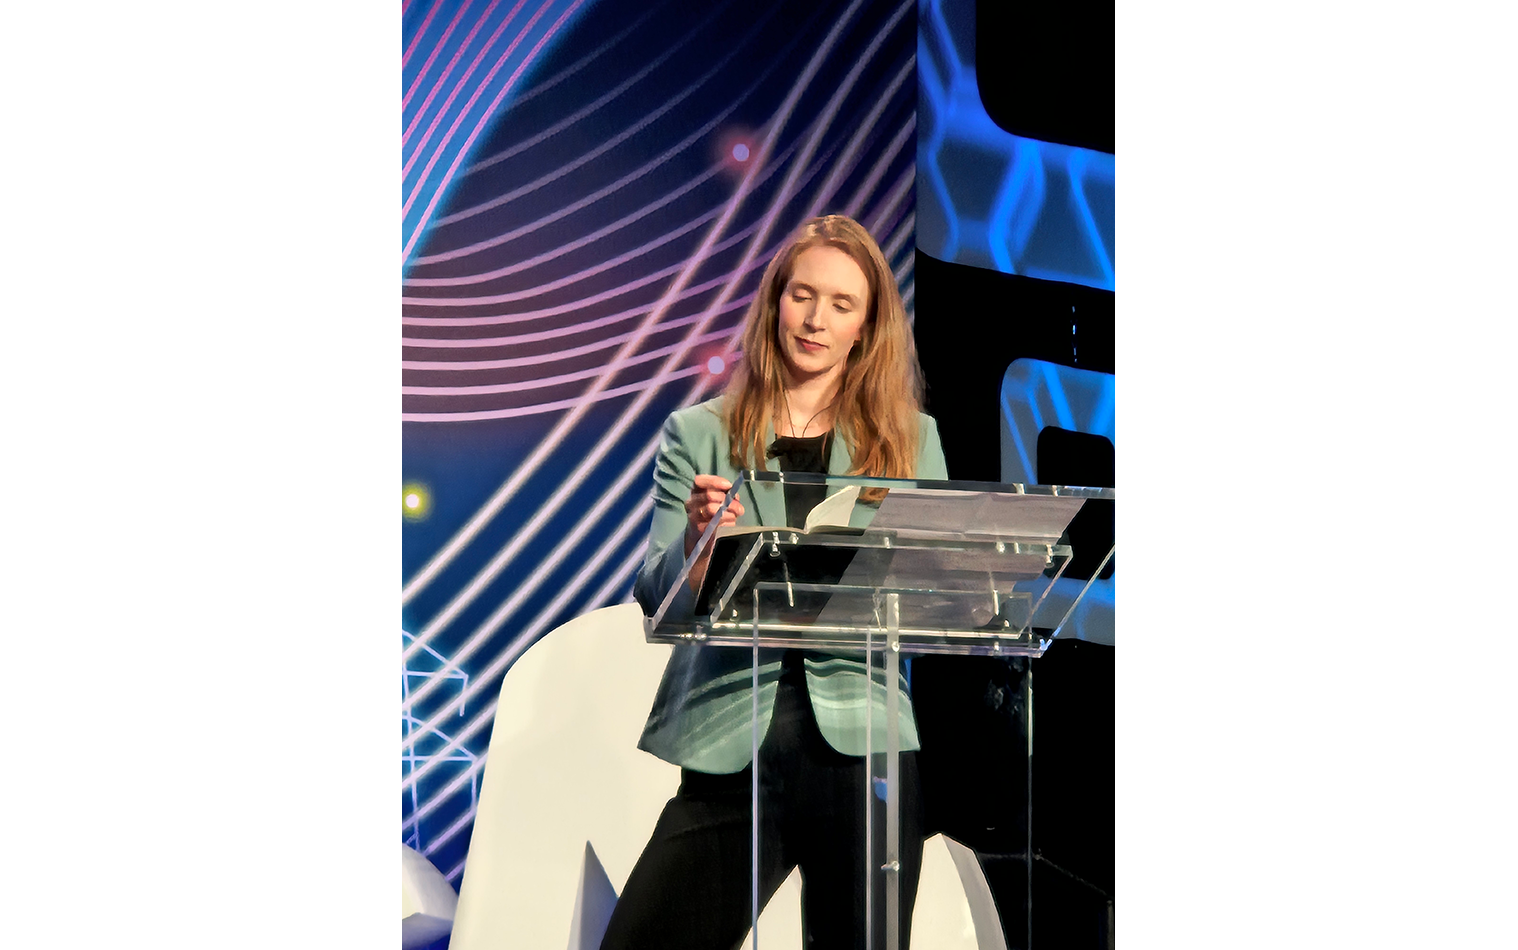
ISA Fellow Sarah Fluchs: Making Cybersecurity Accessible for Engineers
ISA Fellow Sarah Fluchs is bridging the gap between engineering and cybersecurity, making cybersecurity more accessible, proactive and measurable. -
A Look at Two Cyber Reporting Processes: EU CRA and US CIRCIA
Cyber incident reporting is entering a new phase on both sides of the Atlantic. -
Moxa Demonstrates Readiness for Cyber Resilience Act’s 24-hour Vulnerability and Incident Reporting Obligations
This regulation shifts vulnerability and incident handling from an internal practice to a legal obligation that mandates rapid detection, assessment, coordination and regulatory response. -
KUKA Becomes First to Achieve Security Level 2 Certification for Robotics Industry
The certification demonstrates KUKA's commitment to developing automation solutions that meet evolving cybersecurity requirements while assisting manufacturers in protecting critical production assets. -
Securing a Safer Foundation for AI in Food and Beverage Manufacturing
Governed Industrial AI for connected work takes the risk out of AI integration while inspiring frontline workers to work smarter. -
ISA Podcast Shares Insights into Cybersecurity of Water Infrastructure
In this episode of Podomation, panelists discuss cybersecurity in the water/wastewater sector in the context of recent incidents in the US. -
Ransomware Reaches 2026 High in July, Up by 22%
Ransomware volume rose 22% month-on-month, with 894 cases recorded in July 2026. -
ISA and Operational Technology Cybersecurity Coalition Announce Partnership to Advance OT Cybersecurity
The goal is to encourage better implementation and recognition of foundational cybersecurity standards like ISA/IEC 62443, the globally recognized consensus-based series of OT cybersecurity standards developed by ISA. -
The Operational Technology Cybersecurity Coalition Calls for Unified Global Standard to End Regulatory Fragmentation in OT Cybersecurity
The coalition urges U.S. policy makers to formally recognize ISA/IEC 62443 as the foundation for critical infrastructure security. -
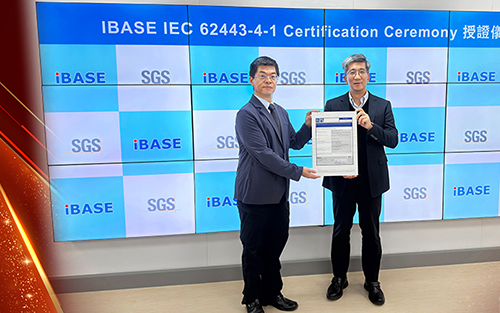
IBASE Achieves ISA/IEC 62443-4-1 Certification to Strengthen Product Cybersecurity
This achievement further strengthens product security, reliability and long-term support, enabling IBASE to deliver more secure, stable and trusted industrial computing solutions to customers worldwide. -
Unraveling Cybersecurity Myths in Chemical Manufacturing: A Path to Safer, More Resilient Operations
Here are some common ISA/IEC 62443 myths that still trip up chemical manufacturers. -
Cybersecurity in US Water Systems: Lessons from the Recent Incidents
While compliance asks, “Have we satisfied the requirement?” risk management asks, “Have we meaningfully reduced the likelihood or consequence of a cyber incident?” These rarely produce the same answer. -
ArmorCode Advances Agentic Vulnerability Remediation with Risk Discipline and AI Cost Savings
“Finding vulnerabilities was never the hard part,” said Mark Lambert, chief product officer at ArmorCode. “The challenge is understanding which findings create real attack paths and what actions will reduce risk."